- Published on
OpenCode Hacked: BYOK Console Credentials Leaked & The "Distillation" Excuse
- Authors
- Name
- Hoang Nguyen
👤 1. Who Is Involved & Impacted?
- Organization Behind the Breach: OpenCode (
@opencodeon X /anomalyco/opencodeon GitHub), creators of the popular open-source terminal coding agent (OpenCode CLI / TUI / Desktop) and its commercial hosted web companion (OpenCode Console / Zen). - Impacted Users (
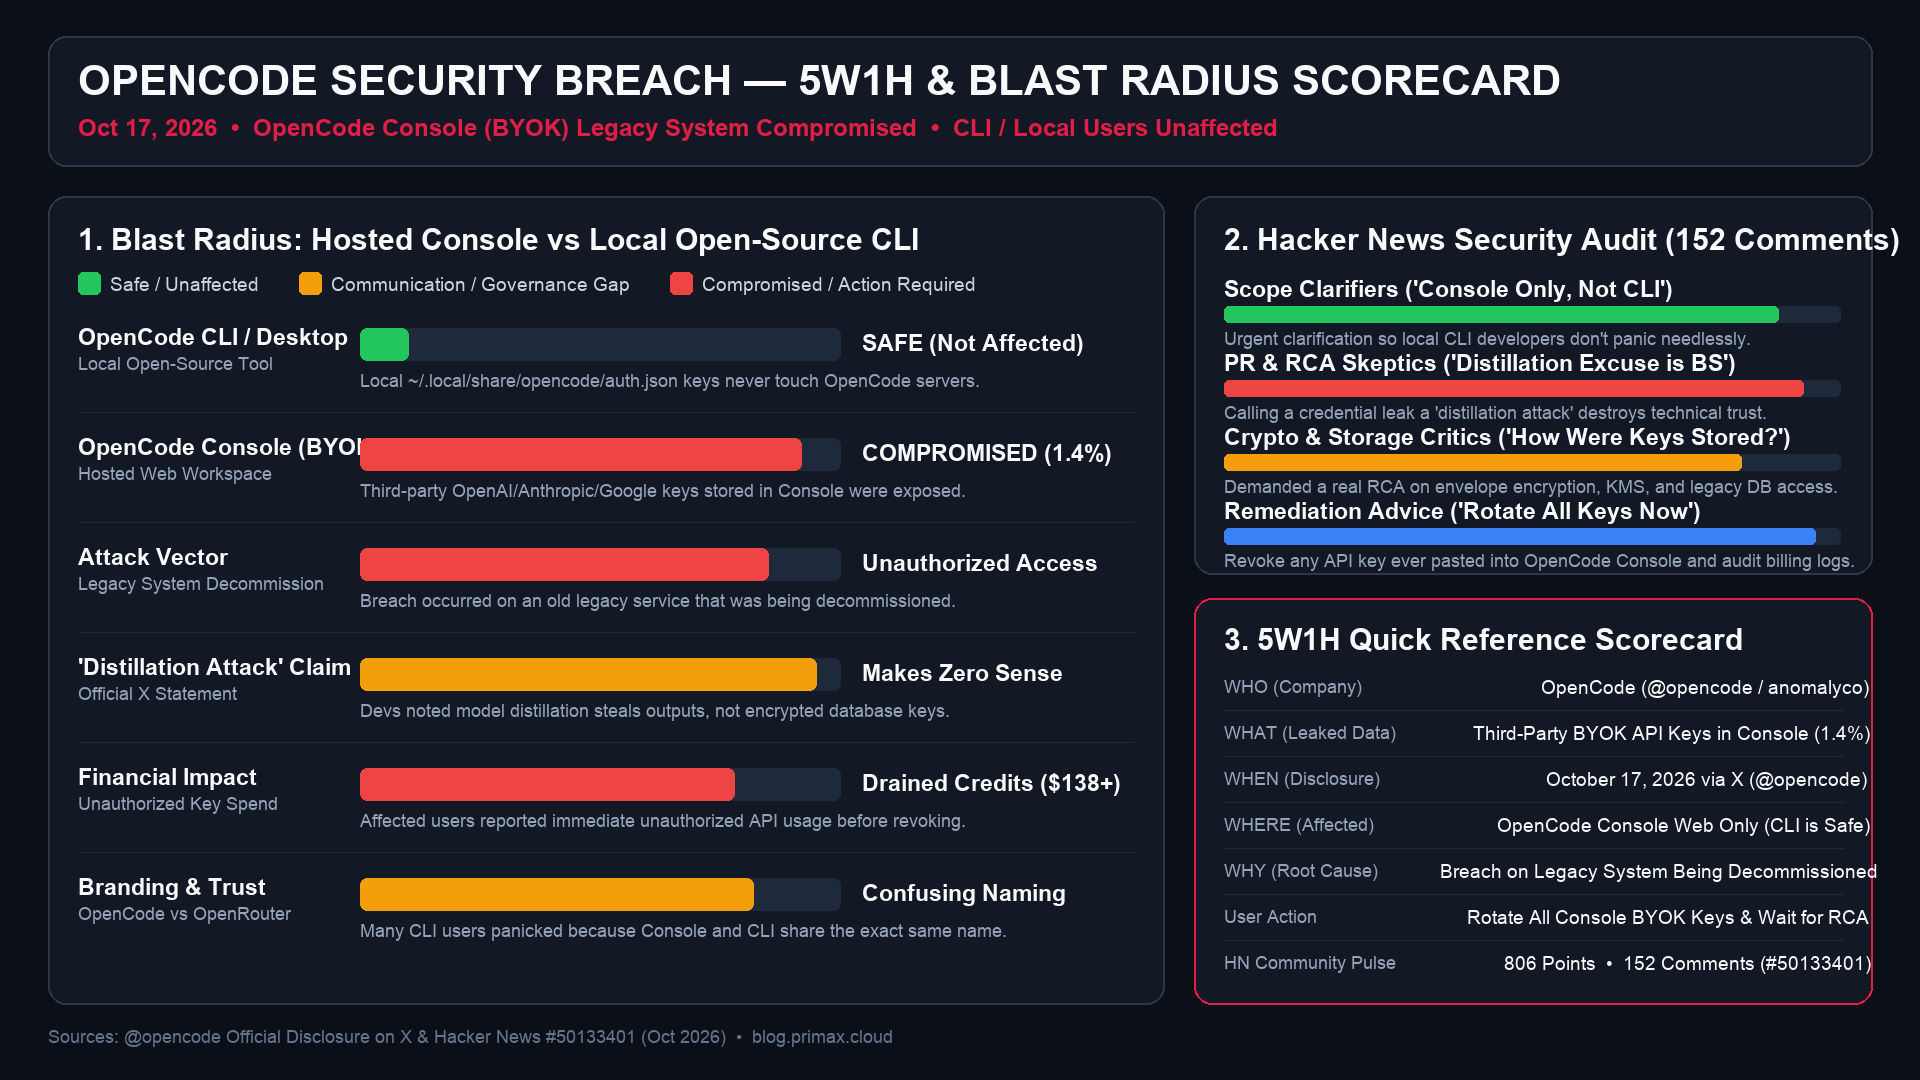
1.4%of Console Accounts): Developers and teams who created an account on the hosted OpenCode Console web platform and stored Bring-Your-Own-Key (BYOK) third-party API keys (OpenAI, Anthropic, Google Gemini) inside cloud workspaces. - Unaffected Users (Local CLI Only): Developers who only run the open-source OpenCode CLI, TUI, or Desktop app locally without logging into a hosted OpenCode Console workspace (local keys live in
~/.local/share/opencode/auth.jsonand never touch OpenCode's servers).
📦 2. What Happened in the OpenCode Breach?
On October 17, 2026, OpenCode disclosed a security breach in which attackers gained unauthorized access to stored third-party LLM API keys:
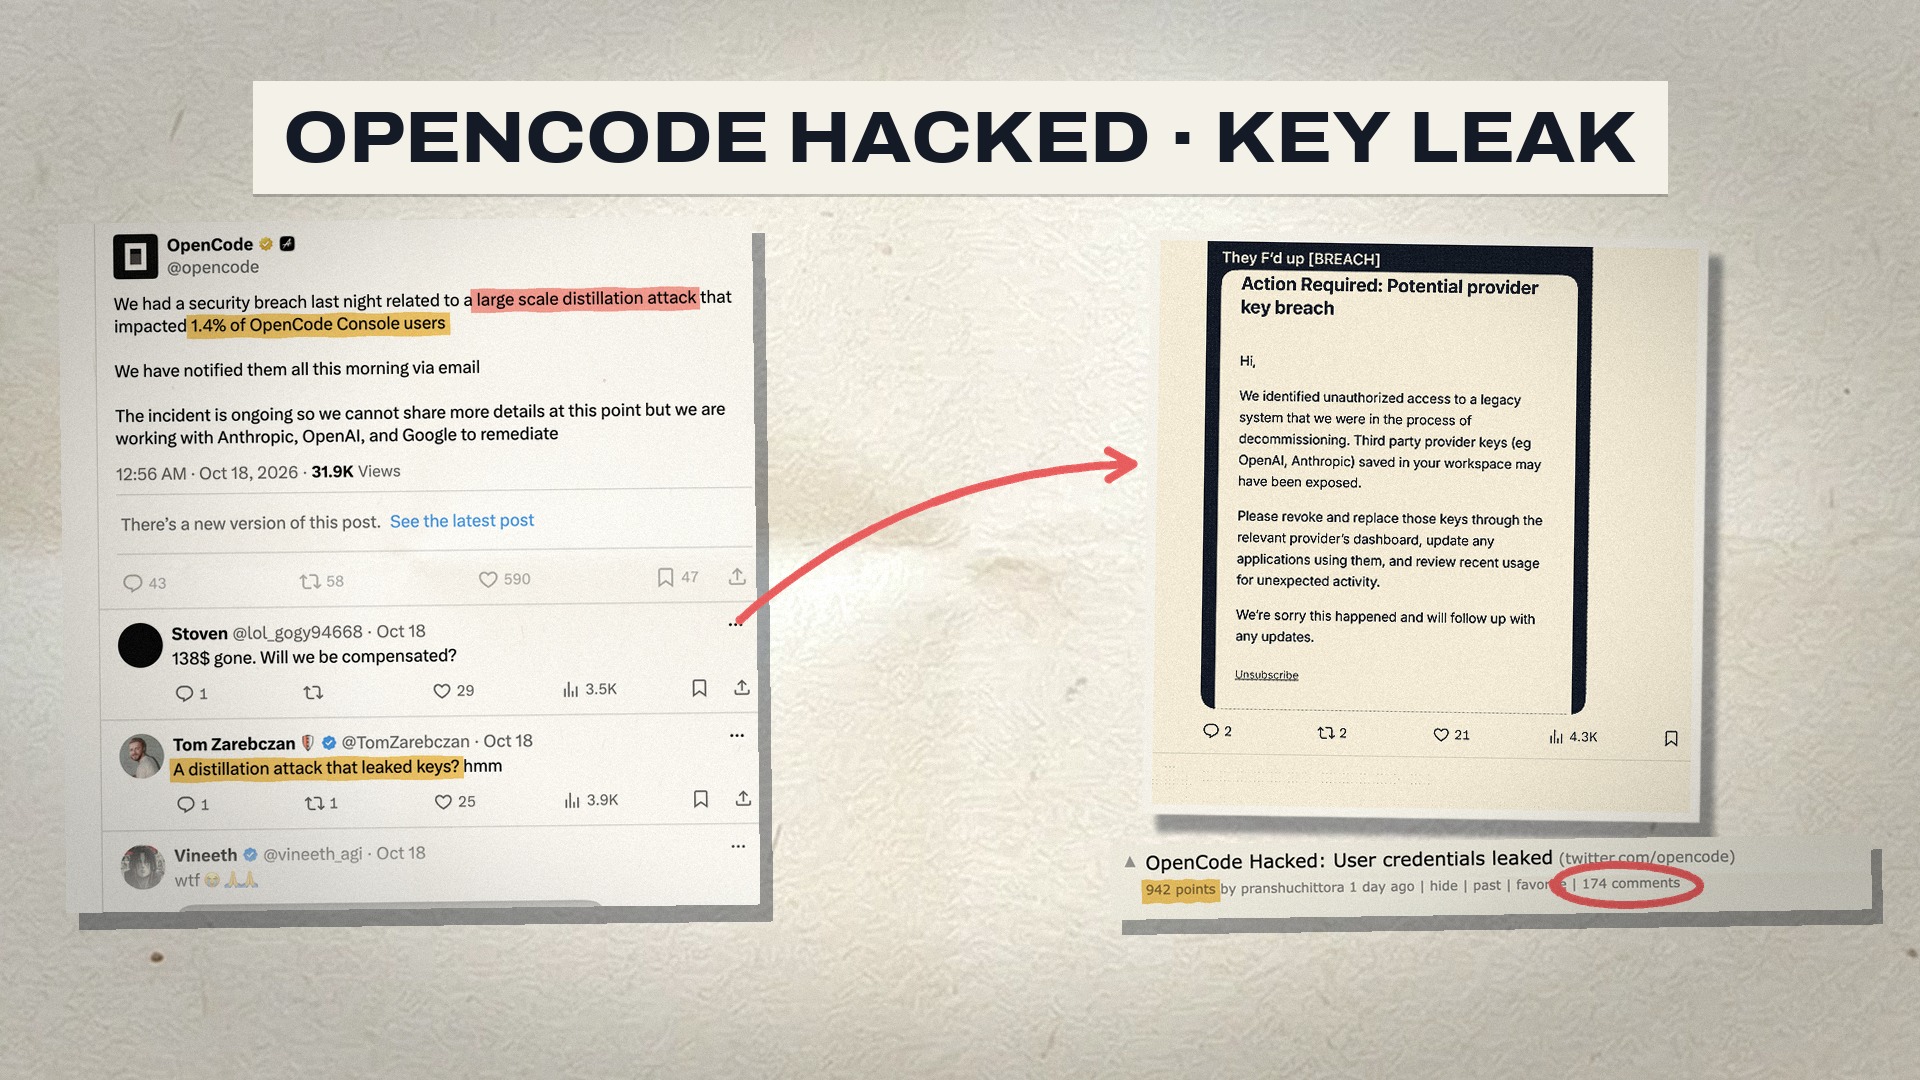
- Legacy System Decommission Compromise: According to OpenCode's disclosure, attackers exploited unauthorized access on an older legacy system that was in the process of being decommissioned, exposing third-party BYOK provider keys saved in workspaces for 1.4% of OpenCode Console users.
- Active Financial Drain Reported: Affected developers on Hacker News (
TomZarebczanand others) confirmed that attackers immediately began draining stolen keys—burning through$138+in prepaid OpenAI/Anthropic API credits within hours until keys were manually revoked. - The Baffling "Distillation Attack" Claim: In its official statement, OpenCode attributed the breach to "an increase in malicious activity related to a large scale distillation attack"—an explanation that baffled security engineers across Hacker News.
- Confusing Product Naming Panic: Because the open-source local agent (OpenCode CLI) and the hosted OpenRouter-style billing/workspace gateway (OpenCode Console) share the exact same brand name, thousands of local CLI users initially panicked believing their local environment variables had been exfiltrated.
📅 3. When & Where?
- When: Disclosed publicly on October 17, 2026, after affected Console users began noticing unauthorized spikes in their OpenAI and Anthropic billing dashboards and receiving security notification emails.
- Where: Announced via @opencode on X (Status #2111516673953935833) and debated intensely on Hacker News (#50133401) with 806 points and 152 comments.
🎯 4. Why Did OpenCode's Response Spark Backlash on Hacker News?
- "Distillation Attack" Makes Zero Cryptographic Sense: Model distillation is when someone queries an LLM API at scale to train a student model. By itself, a distillation campaign cannot explain how attackers bypassed backend authentication and decrypted stored BYOK database secrets—unless attackers specifically targeted OpenCode's database to steal customer API keys in order to fund free distillation runs.
- Questions Over Key Storage & Envelope Encryption: Security engineers (
lifeisloving,latchkey,fleshers) questioned why a legacy system being decommissioned still held live access to production BYOK workspace secrets or KMS decryption keys. - Missing Governance & Transparency: Commenters (
Ciantic,pranshuchittora) pointed out that OpenCode's website lacked clear Terms of Service, Privacy Policy, corporate entity disclosure, or public security architecture docs for how BYOK credentials are encrypted at rest.
⚙️ 5. How Did the Community Respond & What Should Users Do Now?
The 152-comment Hacker News thread converged on three immediate takeaways for developers:
- 1. Separate CLI from Console (
redsymbol,rozenmd): If you only use the open-sourceopencodebinary locally in your terminal with your own.envor localauth.jsonand never pasted keys into the web OpenCode Console, your keys were not exposed in this server breach. - 2. Rotate Every Console-Linked API Key Immediately: Any developer who ever pasted an OpenAI, Anthropic, Google, or OpenRouter key into an OpenCode Console workspace should revoke and rotate those keys immediately, regardless of whether they received an email for the
1.4%cohort, and audit provider usage logs for unauthorized completions. - 3. Demand a Real Technical Post-Mortem (RCA): Developers urged OpenCode to replace vague AI buzzwords ("distillation attack") with a transparent Root Cause Analysis (RCA) detailing the exact attack vector, encryption-at-rest design, legacy system lifecycle, and blast-radius verification.
✅ CONCLUSION
Most agree that only OpenCode Console (BYOK) was compromised rather than the CLI, but OpenCode handled communication poorly and its "distillation attack" story fails to explain why keys were leaked—rotate your keys immediately and wait for a real RCA.