- Published on
OpenCode Hacked: BYOK Console Credentials Leaked & The "Distillation" Excuse
- Authors
- Name
- Hoang Nguyen
👤 1. Who Is Involved & Impacted?
- Organization: OpenCode (
@opencodeon X /anomalyco/opencodeon GitHub), makers of the open-source terminal coding agent (OpenCode CLI / TUI / Desktop) and hosted web platform (OpenCode Console / Zen). - Impacted Users (
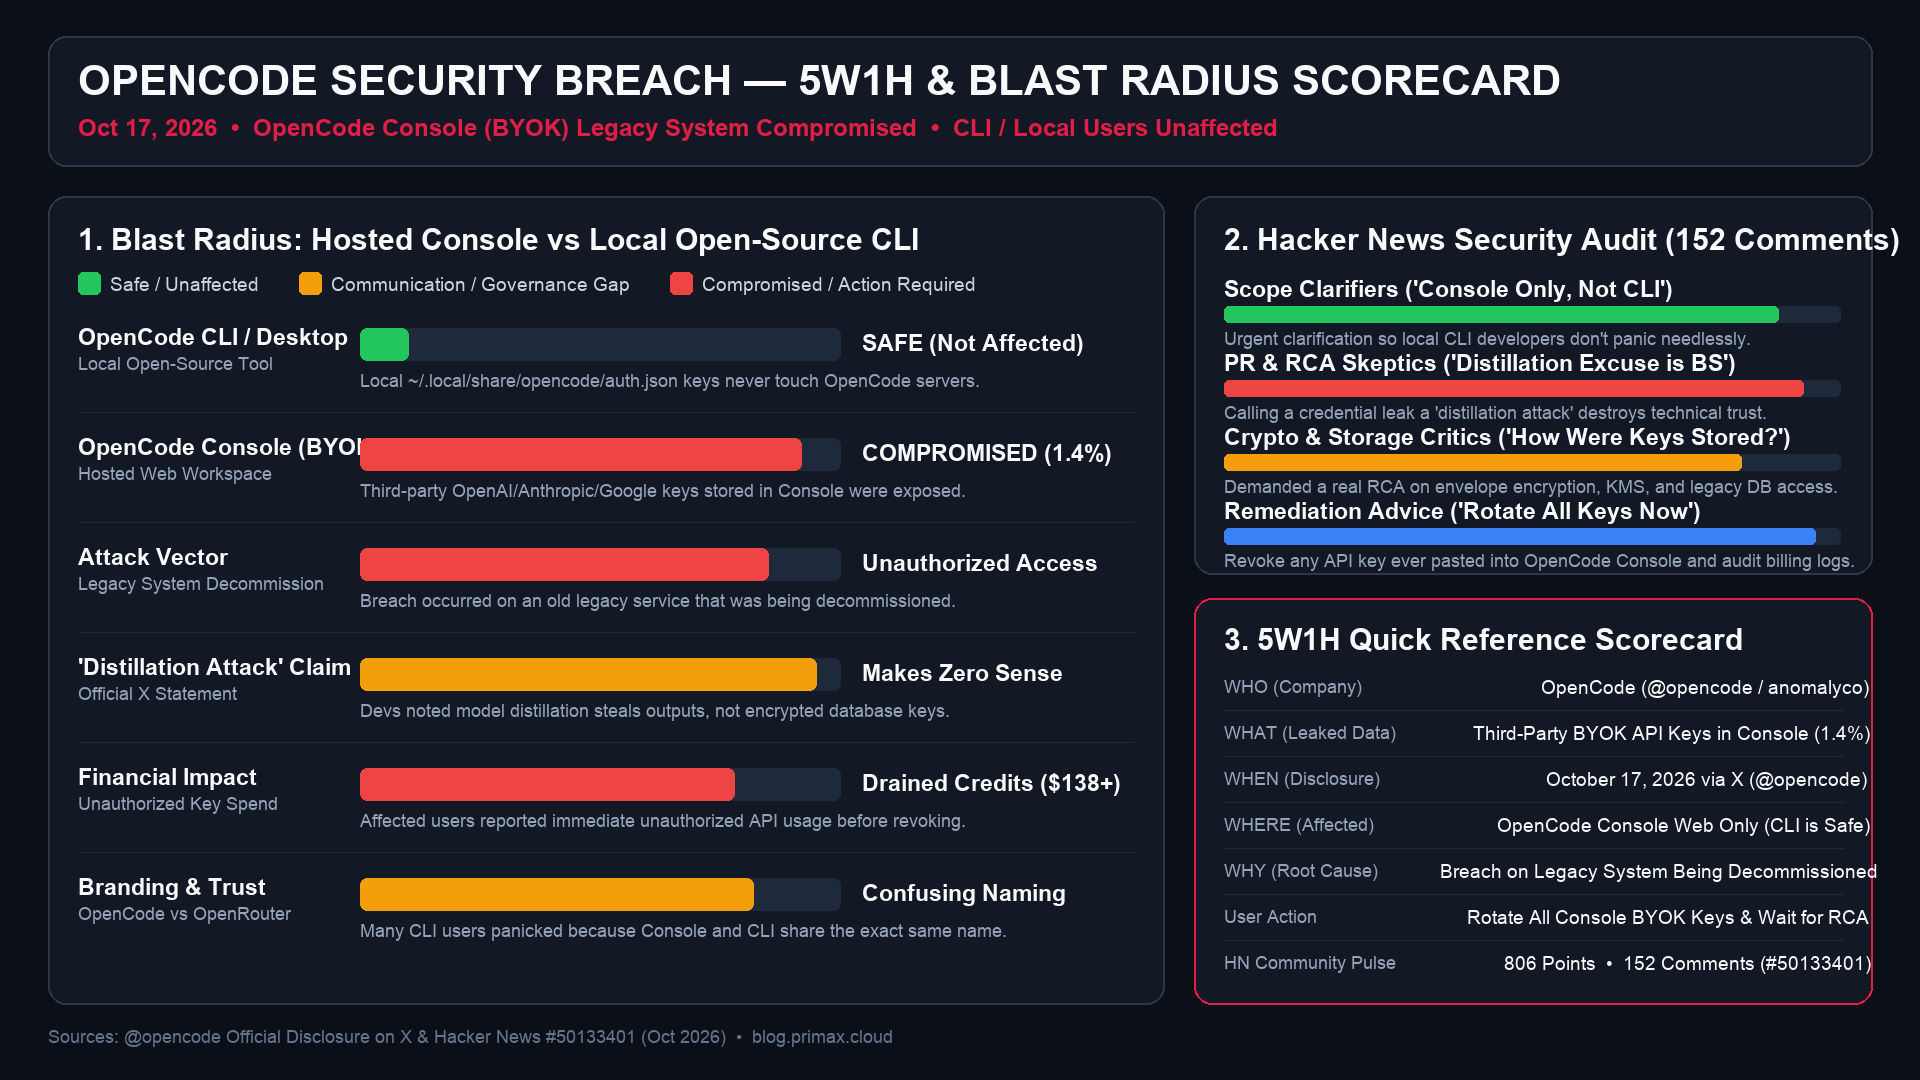
1.4%of Console Accounts): Developers who stored Bring-Your-Own-Key (BYOK) third-party API keys (OpenAI, Anthropic, Google Gemini) inside hosted OpenCode Console cloud workspaces. - Unaffected Users (Local CLI Only): Developers who only run the open-source OpenCode CLI/TUI/Desktop locally without syncing to an OpenCode Console workspace (local keys remain in
~/.local/share/opencode/auth.json).
📦 2. What Happened in the Breach?
On October 17, 2026, OpenCode disclosed a security incident exposing stored third-party LLM API keys:
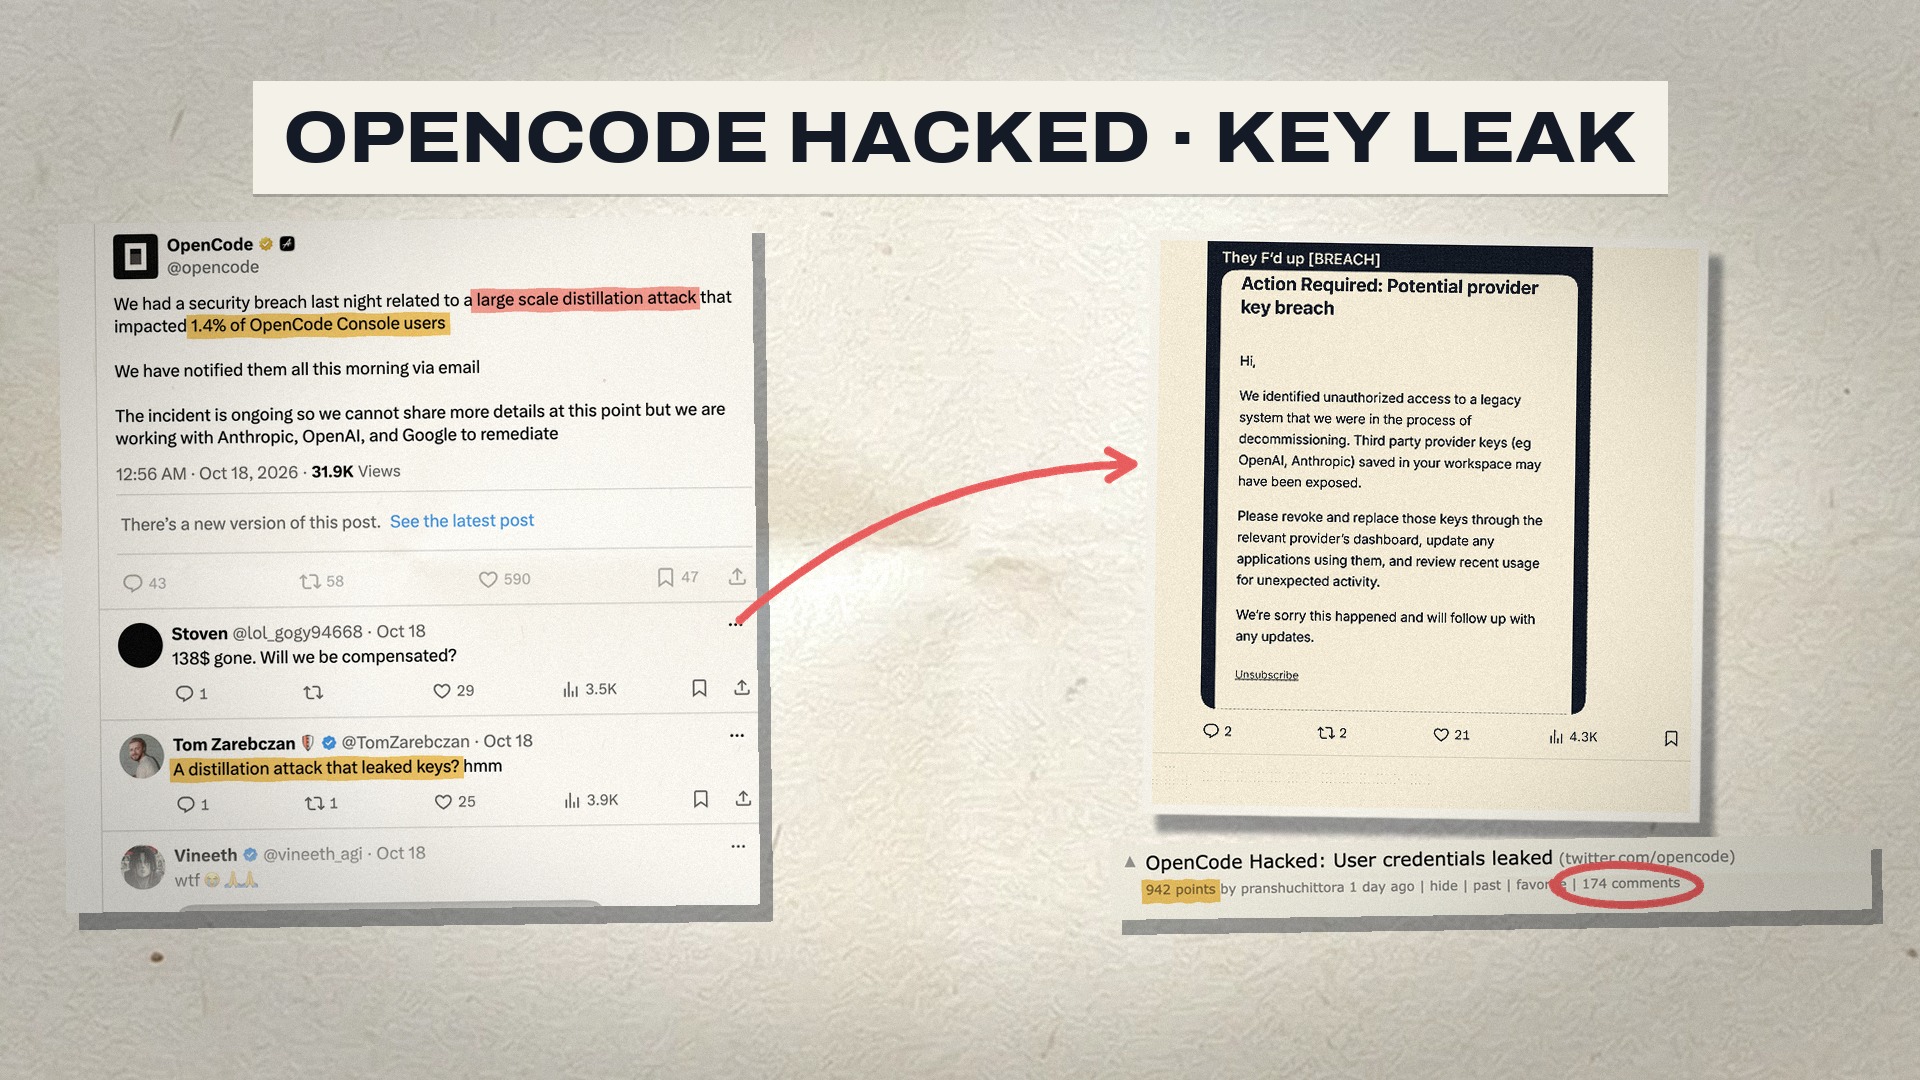
- Legacy Server Compromise: Attackers gained unauthorized access to an older legacy system being decommissioned, exposing BYOK workspace keys for 1.4% of OpenCode Console users.
- Immediate API Credit Drain: Affected developers on Hacker News (
@TomZarebczanand others) reported attackers burning through$138+in prepaid OpenAI/Anthropic credits within hours until keys were manually revoked. - The "Distillation Attack" Excuse: OpenCode attributed the breach to "an increase in malicious activity related to a large scale distillation attack"—a claim that drew immediate skepticism from security engineers.
- CLI vs. Console Brand Confusion: Sharing the name
OpenCodeacross both the local open-source CLI and the hosted Console caused widespread panic among local CLI users who thought their local environment variables were leaked.
📅 3. When & Where?
- When: Disclosed on October 17, 2026, after Console users noticed unauthorized billing spikes on their OpenAI and Anthropic dashboards.
- Where: Announced via @opencode on X and discussed on Hacker News #50133401 (806 points, 152 comments).
🎯 4. Why Did OpenCode's Response Spark Backlash?
- "Distillation" Explains the Motive, Not the Breach: Model distillation is querying an LLM at scale to train another model. It explains why thieves wanted free API keys, not how attackers breached OpenCode's backend and decrypted stored BYOK secrets.
- Decommissioned Server Still Held Secrets: Engineers (
@lifeisloving,@latchkey,@fleshers) questioned why a legacy server being retired still had access to live production workspace credentials or KMS decryption keys. - Missing Security Documentation: Commenters (
@Ciantic,@pranshuchittora) noted the lack of clear Terms of Service, Privacy Policy, corporate entity disclosure, or public documentation on encryption at rest.
⚙️ 5. Incident Breakdown & Community Reaction
| Dimension | OpenCode CLI / TUI (Local) | OpenCode Console (Hosted Web) | Recommended Action |
|---|---|---|---|
| Credential Storage | Local ~/.local/share/opencode/auth.json | Cloud workspace DB (legacy server hit) | Audit whether you ever logged into Console |
| Blast Radius | 0% (Unaffected) | 1.4% of Console accounts | Revoke & rotate all Console-linked keys |
| Reported Loss | $0 | $138+ per drained key in hours | Check OpenAI / Anthropic usage logs |
| Official Explanation | N/A | "Large scale distillation attack" | Demand a full technical post-mortem (RCA) |
- The
"OpenCreds"Roast: HN commenters joked that blaming a database leak on a "distillation attack" earned OpenCode an instant rebrand to "OpenCreds." - Separate Local CLI from Hosted Console (
@redsymbol,@rozenmd): Local terminal users who never pasted keys into the web Console were not exposed by the server breach. - Rotate First, Ask Later: Security engineers advised rotating any API key ever entered into OpenCode Console regardless of whether you received an email for the
1.4%cohort.
✅ CONCLUSION
Only the hosted OpenCode Console (BYOK) was breached rather than the local CLI, but blaming a server credential leak on a "distillation attack" explains the attackers' shopping list rather than the broken lock—rotate any Console-linked API keys immediately.